

Why You Should Use a Security Harness for Enterprise AppSec
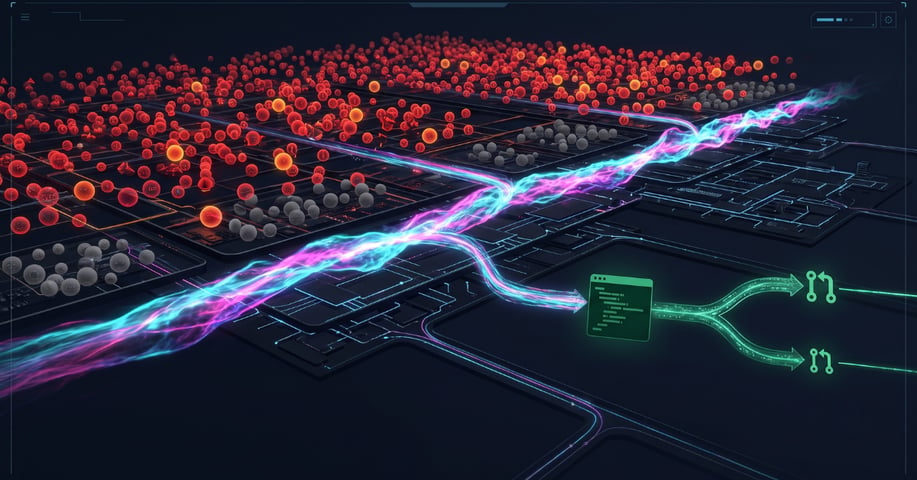
Application security teams do not have a detection problem. They have a triage and remediation problem. If you deploy modern SAST, DAST, and SCA tools, they will do exactly what you pay them to do: find thousands of potential vulnerabilities across your codebase.
Related resources:
Explore the agentic AI cybersecurity platform
Compare agentic security harnesses
The problem begins the moment those scans finish. A spreadsheet containing five thousand critical and high vulnerabilities is a liability, not a solution. When standard scanners lack the context of how your application actually runs in production, they flag everything. This creates massive alert fatigue, forces security engineers into endless manual triage, and creates friction with development teams asked to fix bugs that were never actually exploitable.
This operational bottleneck is exactly why engineering organizations are shifting their architecture. To bridge the gap between finding a flaw and actually fixing it, modern teams deploy an agentic security harness.
What Is an Agentic Security Harness?
Before evaluating the benefits, it helps to define the architecture. An agentic security harness is a centralized orchestration platform built specifically for security engineers. It sits directly on top of your existing security scanners and integrates natively into your developer workflows and code repositories.
Unlike a scanner that relies on static rules to find known signatures, a harness acts as an active execution engine. It uses AI agents to ingest raw alerts from any source, perform deep contextual analysis to filter out the noise, and execute complex security workflows.
Raw AI is not enough on its own. Large language models understand code syntax and can spot a vulnerability if you paste a snippet into a chat window, but they lack the contextual awareness of your specific application architecture: your internal coding standards, your library versions, how a suggested fix might break a downstream dependency. Left unchecked, that gap produces hallucinated fixes that fail to compile or quietly introduce new flaws. A standalone AI model is a powerful engine, but an engine without a chassis, steering, and brakes is dangerous. The harness is that chassis: the surrounding infrastructure that makes the model safe, predictable, and effective for enterprise application security.
The Core Problem: Alert Fatigue by the Numbers
To understand why you need a harness, look at the limitations of standard scanning tools. Generic scanners rely on vendor-provided CVE lists. They scan your code or dependencies and match them against those lists, but they do not understand your business logic. They do not know if a specific vulnerable function inside a library is ever actually called by your application, or whether it is exposed to untrusted input.
Because the scanner lacks execution context, it alerts on everything, and the numbers add up fast:
- The industry average ratio of developers to security engineers frequently sits at one hundred to one.
- Up to seventy percent of the alerts a standard SAST scan generates can be false positives or low-priority noise.
- Many security teams spend more than twenty percent of their week manually closing out alerts that were never exploitable in the first place.
Security engineers are forced to manually trace execution paths to figure out which findings are real. This manual triage takes hours per alert. Meanwhile, development is blocked, and the real threats hide in the noise.
Why You Should Use a Security Harness
Deploying a security harness changes the daily operations of both your security and development teams. Here are the core reasons enterprise AppSec teams adopt one.
Understanding AI security harness capabilities helps teams evaluate which functions improve security operations, from contextual triage to automated remediation and policy enforcement.
1. Contextual Triage and Reachability Analysis
The most significant drain on a security team is manual triage. A harness performs automated reachability analysis: it maps the execution paths of your entire application, and when a scanner flags a vulnerable library, AI agents trace the data flow to determine whether that library is actually loaded into memory and reachable from external input.
If the vulnerability is unreachable, it poses no real risk to the business, and the harness automatically suppresses or deprioritizes the alert. This mathematical approach to context eliminates a huge share of manual triage and ensures developers only spend time on verifiable, reachable threats.
2. Automated Vulnerability Remediation
Visibility alone does not secure an application. When a harness verifies a true positive, it does not just open a ticket. It uses AI agents to understand the specific framework, syntax, and style of your local codebase, generates the exact code required to patch the flaw, and submits it as a standard pull request directly into GitHub or GitLab.
The developer reviews the AI-generated code, confirms it passes standard unit tests, and clicks approve. This drastically reduces mean time to remediation, turning a fix that used to age in a backlog for months into something resolved in minutes.
3. Deterministic Validation Before a Human Ever Sees It
Automating remediation only works if the output can be trusted. Before a fix reaches a pull request, a mature harness runs it through validation: it confirms the code compiles, and it verifies the change actually resolves the specific alert that triggered the workflow in the first place. If a proposed fix fails validation, the harness rejects it or sends the AI back with feedback on exactly why, rather than passing a broken suggestion on to a developer to catch.
4. Custom Detection Agent Deployment
Generic rules only catch generic bugs. Standard scanners are necessary for baseline security and compliance, but they miss proprietary business logic flaws unique to your architecture.
A harness lets security engineers deploy custom detection agents in minutes. If your threat modeling identifies a specific architectural anti-pattern, an unauthorized API data exposure, or a custom authorization bypass risk, you configure an AI agent within the harness to search your entire codebase for that exact logic flaw. You stop waiting for a vendor to update their CVE list and start hunting for what actually matters to your business.
5. Elimination of Custom Maintenance Debt
Historically, engineering teams tried to solve this with custom scripts: assigning DevOps engineers to write API integrations pulling data from various scanners into a central database. That approach creates massive maintenance debt, because vendors constantly update their APIs and alter their JSON output formats, breaking the internal scripts every time. A commercial harness eliminates this burden entirely; the vendor manages all tool integrations natively, and your engineering team goes back to building product instead of maintaining fragile plumbing.
6. Security Guardrails and Policy Enforcement
Bringing AI into a security workflow requires strict control. An effective harness surrounds AI agents with strict boundaries, deep environmental awareness, and API controls. Security teams define the rules, for example that an agent can automatically close low-severity informational alerts but must draft a pull request and request human review for any critical code change, and the harness enforces those rules automatically, preventing the AI from hallucinating a command or altering a production firewall.
When an agent hits an edge case or falls below its confidence threshold, it routes the investigation to a human engineer with the evidence collected and a recommended action, cutting manual investigation time drastically.
7. Consistent, Round-the-Clock Policy Application
Human reviewers are subjective and prone to fatigue. A harness applies your security policies consistently across every line of code and every pull request, at any hour, ensuring standard remediation patterns are applied universally rather than left to a tired reviewer's judgment call.
8. A Unified Developer Experience
Developers experience security fatigue when they have to log into multiple portals to understand their tasks: one dashboard for the SAST vendor, another for the SCA tool, a third for the cloud provider. A harness centralizes all findings into a single data model and delivers the information, and the fix, directly into the developer's native environment, whether that's GitHub, GitLab, or Jira. This reduces friction and builds a culture of shared responsibility between security and engineering.
Not Just a Dashboard: How a Harness Differs from ASOC and SOAR
It is easy to confuse this category with legacy orchestration tools. The distinction matters for your architecture.
Application Security Orchestration and Correlation (ASOC) platforms aggregate scanner data, deduplicate it, and put it on a dashboard. They create tickets for humans to resolve. They are passive databases.
Security Orchestration, Automation, and Response (SOAR) platforms operate on deterministic logic, simple "if this, then that" rules. That works for blocking an IP address, but it fails completely with the nuance of software vulnerabilities: the same flaw might be critical in one microservice and irrelevant in an internal test environment, and a fixed playbook cannot tell the difference.
Comparing an agentic security harness to either of these is like comparing an autopilot system to a dashboard warning light. An agentic harness is an active participant in your workflow. It does not just aggregate or route data, it investigates the validity of the data through reachability analysis and actively writes the code to resolve the issue. If your current tool requires a human to write the patch, you are using legacy technology.
Where This Fits in Your Pipeline
The idea of a "harness" isn't new to software engineering. A classic test harness is a collection of software and test data configured to run a program unit under varying conditions and monitor its behavior, much like a construction worker's safety harness arrests a fall before it becomes a catastrophe. A security harness applies that same idea to vulnerability detection: it integrates SAST, DAST, SCA, and fuzzing into a unified, automated workflow that triggers on every commit rather than running manually or on a quarterly audit cycle. When a pull request introduces a critical flaw, the harness can flag it, or block the merge outright, the same way a physical harness arrests a fall before it becomes a fatality.
An agentic security harness builds on that same automated-gate idea, then adds the reasoning, remediation, and guardrails described above on top of it.
How to Roll One Out
Adopting a harness works best as a staged rollout rather than a flip of a switch.
For teams considering a custom implementation, building an agentic security harness involves additional architectural decisions around integrations, agent orchestration, validation, and governance.
Establish your baselines first. Before turning on automated remediation, measure your current MTTR and false positive rate. Run the harness in observation mode so it learns your codebase and proves its accuracy before it starts acting on your behalf.
Integrate where developers already work. The output should appear as standard pull requests and inline comments in GitHub, GitLab, or Bitbucket, not a separate dashboard developers have to remember to check.
Scale gradually. Start by enabling automated pull requests for low-severity issues, and only expand to critical vulnerabilities once your team trusts the output.
Prioritize accuracy over volume. A harness that constantly blocks builds over non-exploitable findings will get bypassed. Tune for precision from day one.
Signs Your AppSec Program Needs This Now
- Your security team spends more than twenty percent of its week manually closing false positives.
- Your vulnerability backlog grows larger every quarter despite adding new security headcount.
- Developers routinely ignore security tickets because they lack context or actionable fix instructions.
- You employ full-time engineers solely to maintain custom API integrations between security tools.
If these symptoms exist in your organization, your current architecture is failing to scale.
Frequently Asked Questions
Does a security harness replace my existing SAST, DAST, and SCA tools? No. A harness sits on top of your existing scanners. It ingests their findings and provides the contextual triage, reachability analysis, and automated remediation those tools don't do on their own.
Is automated remediation safe for production code? Yes, because the harness never merges code automatically. It generates a pull request, and a human developer always reviews and approves the change before it merges into the main branch.
How does a harness handle our proprietary internal frameworks? Advanced platforms learn the specific patterns and syntax of your codebase over time, so suggested fixes align with your internal coding standards rather than generic best practices.
What is the difference between a security harness and a penetration test? A harness is a continuous, automated testing environment built into your pipeline. A penetration test is a manual, point-in-time assessment by human experts. Both matter, but the harness provides daily protection between pen tests.
Can a security harness replace our AppSec team? No. It automates the routine, high-volume work: triaging noisy alerts and drafting boilerplate fixes. It frees your engineers to focus on complex threat modeling and architectural security decisions.
Conclusion
Securing enterprise software requires more than finding flaws. It requires a system capable of contextualizing risk and automating the repair process. You can't hire your way out of a scanner backlog. You have to automate the resolution process.
By sitting between your scanners and your source code, an agentic security harness transforms raw security alerts into deployment-ready code fixes. It eliminates manual triage, accelerates remediation, and aligns the goals of your security and development teams.
Ready to upgrade your AppSec operations? Apply for early access to Amplify Console and see how an agentic security harness can transform your vulnerability management today.
Subscribe to Amplify Weekly Blog Roundup
Subscribe Here!
See What Experts Are Saying
BOOK A DEMO
Jeremiah Grossman
Founder | Investor | Advisor
Saeed Abu-Nimeh
CEO and Founder @ SecLytics
Kathy Wang
CISO | Investor | Advisor
Alex Lanstein
Chief Evangelist @ StrikeReadyFrequently
Asked Questions
What is vulnerability management, and why is it important?
Why is vulnerability management important?
What makes vulnerability management extremely challenging in today’s high-growth environment?
How can Amplify help me with vulnerability management?
What technology does the Amplify platform integrate with?
Have a
Questions?
Contact Us
Ready to
Get started?
Book A GUIDED DEMO
